Audit logs
Every sensitive action, attributed and timestamped, streamed to your own SIEM
Membership changes, project deletions, credential rotations, and more, recorded automatically and filterable in-app on every plan; optionally streamed live to your own security tooling, HMAC-signed so it can prove where it came from.
Recorded automatically, attributed to a real actor
An audit log entry carries who did it (actor_email), what (a plain action string like project.deleted or project.api_key_rotated), what it was done to, when, and from what IP address, plus whatever extra detail that specific action wants to carry. Nothing here depends on an admin remembering to log anything; it's written at the same moment the sensitive action itself happens, inside the same request.
Filterable in-app, on every plan
An organization's audit log is searchable by actor or action text, filterable to one specific action, and boundable to a date range, entirely server-side, not a client-side filter over a page that already loaded everything. Every distinct action string that organization's own history actually contains populates the filter dropdown, so it never goes stale as new action types get added over time. Viewing it at all is admin-role and up, but not otherwise plan-gated: this is available on every plan, not held back for Business or Enterprise.
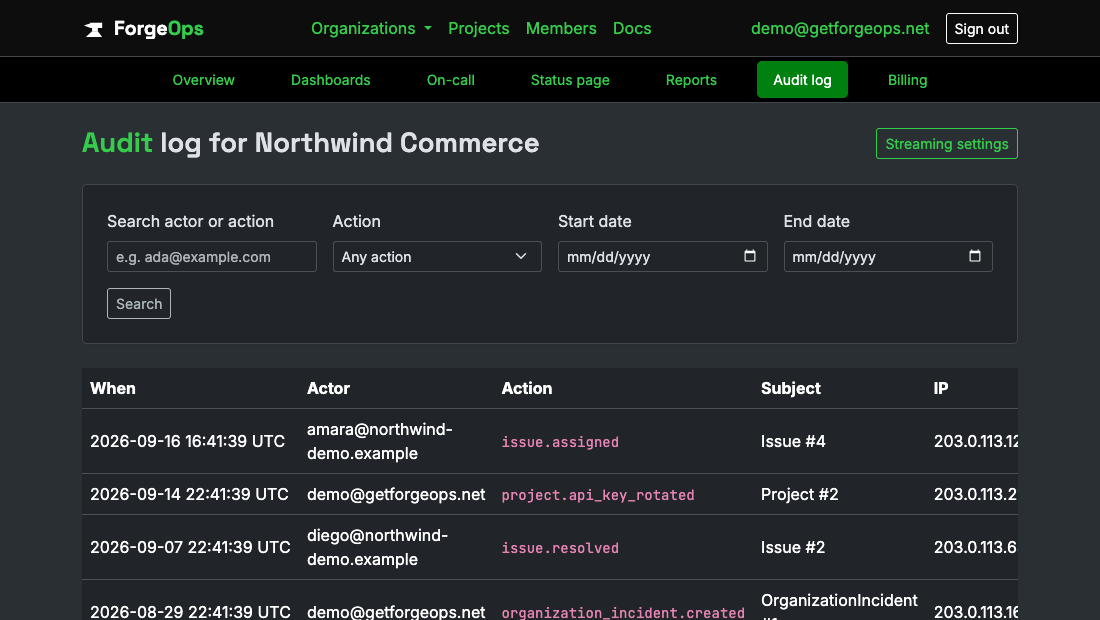
Every sensitive action, attributed to a real actor and timestamped.
Live streaming, with retries a Slack ping doesn't get
Turn on webhook streaming and every new entry posts to your own SIEM/webhook destination the moment it's durably written, HMAC-signed the same way an alerting webhook is, so your endpoint can verify it actually came from ForgeOps rather than trusting whatever hits the URL. Unlike a plain notification delivery (which is allowed to just drop silently on failure), this job explicitly retries on a polynomial backoff, five attempts, before giving up: compliance data has a different reliability bar than a Slack ping, and a transient outage on your own receiving end shouldn't silently cost you an entry forever.
Enterprise plan only, the same tier as on-call scheduling and IP allowlisting: real, ongoing infrastructure on top of the log itself, which every plan already gets to see.